
The Savvy CIO: Episode 5 – “Managing the Spend you Can’t See”
Podcasts
Mark Dunkerley, VP of Enterprise Technology Services and CISO at Coca-Cola Bottlers Sales and Services, sits down with host Bradd Busick to talk through the invisible costs that quietly erode IT budgets: cloud sprawl, unused tools, lingering AI pilots, and emerging token-based AI pricing…not to mention the persistent drain of legacy and technical debt. Mark and Bradd also discuss why the most successful modern CIO and CISO roles are shelving their egos to converge around shared risk ownership, business continuity, and data-driven communication with executives and boards.
But it’s not all sharing-is-caring sunshine and rainbows: they also dig into why rapid technology changes are making long-range budgeting difficult (and by long-range, they mean longer than 6 months); why relational capital built between IT leaders and the business is essential for project funding, and fast due diligence; and why the process side of AI ROI still needs a lot of work to show potential, while user productivity tools are already showing faster value returns – IF adoption is properly managed, that is.
Mark’s key advice that we all can get behind? Businesses need to shift from reactive to proactive governance…and now is finally the time to share the load of accountability beyond the CIO and CISO.


Listen to all episodes of The Savvy CIO here.
'Managing the Spend you Can’t See' Episode Transcript
Mark Dunkerley: I can go back 20 years, and the hidden spend was around just traditional, oh, I need a server, I need storage. And that’s the old school way. All of a sudden, the last five, 10 years, everybody’s transitioned into the cloud. Now today, obviously AI is the biggest one. I don’t think anybody knows how to calculate AI costs. When we’re looking there from top and based costs and also the things we’re trying to figure it out, it’s becoming more and more challenging and we need to move faster and faster, and we need to be able to be as current as possible, and that seems to be very consistent across the board in every organization right now.
Bradd Busick: You’re listening to The Savvy CIO, modernized wisely by Park Place Technologies. I’m your host, Bradd Busick, and this is a show where we talk about budget pressure, AI adoption, security, and the art of keeping the lights on without burning everything down with the people who are tackling these problems every day. There’s lots of visible price tags on the floor when it comes to hardware, things like servers and switches, even the maintenance contracts to keep these things running. You can touch hardware, you can see things like depreciation with your own eyes and plan for it. But just beneath that surface, there’s a whole iceberg of costs that are much harder to keep tabs on. Things like cloud sprawl, AI pilots that never got off the ground, but also never got canceled and are still running around in your environment. Pricey tools that only have three users.
There’s a ton of invisible bleeds. They aren’t going to sink you because they’re big. They’re just going to sink you because you forgot that they were there at all. Mark Dunkerley is the VP of Enterprise Technology Services and CISO at Coca- Cola Bottlers’ Sales & Services, meaning he has one of the most unique vantage points in the industry. He supports nearly 60 Coca- Cola bottlers across North America, so he’s used to navigating stakeholder complexity at scale, and across dozens of distinct business environments.
Mark knows that these days an IT spend is a lot less like a fixed utility bill, and a whole lot more like a cell phone plan from 2008. You think you’re signing up for one thing, but for some reason your bill has 17 different line items that you didn’t even know you were paying for. The pressure’s on to develop projects faster than ever before, and the meter is always running. If you’re not keeping an eye on it, you’ll be in for a big, bad surprise when it’s time to pay the piper. And it could be the CIO or CISO stuck holding the bag if you’re not careful. Mark, welcome to The Savvy CIO.
Mark Dunkerley: Thanks, Bradd. I’m excited to be here.
Bradd Busick: Yeah, so glad to have you, man. Your background is awesome. Just to kick things off, tell me a little bit about yourself. How did you come to this particular role at CCBSS?
Mark Dunkerley: My background originally, you can probably tell from the accent, I live in Florida, but I’m not a native Floridian. I’m from Newcastle, England, and the dream was to be football player. But I came over to the States, went to college on a scholarship to play football, and that pivoted into technology, working with the university and the technology department. Originally working as a network administrator, moved on from that, evolved into the healthcare industry, a lot of the collaboration tools. Naturally, those come with security with it, and I’ve been in different areas of the Coca- Cola system over the 11 years. Originally was to work within the collaboration stack, email management, and those type of tools, and that evolved into different changes within the company that allowed for the opportunities.
The one that really stuck out was the opportunity to go in our business services organization where we were able to build out a whole new infrastructure greenfield from the ground up. And as we went through that, I was more overlooking the architecture. The cybersecurity started kicking in a lot more. You think six, seven, eight years ago, that’s really where the visibility started coming in and started pivoted more towards the cybersecurity side and the opportunity to build a cybersecurity program from the ground up. And that evolved into where I am today with Coca- Cola Bottlers’ Sales & Services. I know there’s traditionally been maybe those focused on security, those focused on IT. I’ve had the opportunity to really come from the IT side into cybersecurity and then really overlook both those different hats right now.
Bradd Busick: That’s amazing. And those worlds are so blurred now when you consider where you and I both started when they were separate. To put it in football analogy, the midfielder needs to be able to play defense, also needs to be able to be a striker. You’ve just seen so much. I’m assuming you start to see patterns. What’s the one thing that you noticed in the first conversation that tells you a lot about where they’re at in their maturation? Because you already know where you need to take them. What things pop out to you?
Mark Dunkerley: If we’re looking from the security side, technology’s been the focus, and obviously the business driver, and then we’ve shifted over the last five years. I think there’s a big gap in understanding the risk that we have within a business, within our environment, and maybe that’s one of the fortunate opportunities I’ve had is that I have more of a risk- first mindset. And even going beyond that technology leader, this is something we as leaders have to work more broadly across the business is that our mindset has to change. We have to figure out how we work with our other business functions, and that when you look at the bottlers and other entities, it’s really helping to drive and understand what that risk is. It tends not to be a first sort of thought. I think it’s getting there because cybersecurity events hit. We’re starting to see what the real impact is. But business continuity and understanding where you are, I think is a big gap in a lot of organizations. I always tend to lean towards and try to understand a bit more.
Bradd Busick: Yeah, I love this, and you’re highlighting something that I think is really important. One, today’s IT leader needs to be just as much of a business person as they are a technologist. And two, I think there’s finally starting to be a recognition giving all of the cyber threats and risk mitigation, particularly emphasis in business resiliency to say, ” What does it cost if I actually close down? What’s my cost per minute?” In a previous world, it cost us $ 10,000 a minute to be down.
Now, when you put it in that term, suddenly when the CIO goes and asks for budget, you’d think leadership would say, ” Do what you need to do to keep us up.”
Not, ” Well, HR is considering this new recruiting module.” It’s like, no, do you even want your organization to be able to recruit? It’s a fundamentally different risk profile and posture, I think, that I hope organizations and boards and leadership are finally starting to see.
Mark Dunkerley: Yeah. Yeah. I think the message getting out there for sure. We talk about hidden costs. We see these costs of a cybersecurity breach, and to your point, I bet you a lot of organizations don’t know what the cost is to be down for a minute. And if you start running those numbers, you’re looking at other costs behind the scenes. What about reputation? What about customer trust and everything else? So it’s definitely something that grows a lot bigger once you start to unpacking what’s part of that broader conversation.
Bradd Busick: Yep. I think that’s brilliant, and part of this becomes forced when an event happens in the role of a CIO or a CISO. I think our coaching would be: let’s get proactive. We want our CIOs and our CISOs to start helping marketing, help leadership, help the board articulate some of those risks that no one cares about until it actually breaks and now you’re in a reactive spot.
Mark Dunkerley: Exactly.
Bradd Busick: Before we maybe get into the weeds on the hidden spend, I think we probably need to set the stage of why this is becoming so common. I once had someone tell me, ” We need IT to stay in your lane.”
And my response was, ” No, let’s actually flip that. You’re on my highway. The entire foundation of the business is technology. And so without tech, you don’t have a business.” I’d love for you to maybe pull the string a little bit on how you’ve seen the role between the CIO and the CISO start to separate or converge.
Mark Dunkerley: Yeah, it’s an interesting one because the function is probably one of our newest organizations, I would say, within the last 10 to 20 years. And although we have had some presence of security, I mean, think the last five, 10 years, it’s really all of a sudden just grown significantly because of requirements, regulation, everything else that comes along with it. And it’s been interesting because organizations have started building cybersecurity functions, security functions.
And then there’s this argument of where does the CISO report into? Should the CISO have a seat at the board? And you’ve got the CIO. I think they’re all very relevant conversations. I think a lot of it depends. I think ultimately at the end of the day, you’ll have a CISO or CIO. I think they can’t work independently, they can’t work separate. And there needs to be some sort of structure that allows both of them to work together, whether they report into one another, or they report into the board.
But if you have the right personnel, CIO and CISO working together, they need to understand each other. I think for the most part, a CIO these days has to have security, cybersecurity skills to be successful. And I think vice versa, I think the CISO, the security leader needs to have those technology and understand those technology skills. So today, these roles need to be working hand in hand. There should be no segregation or competition between what they do. Everything you do in your role is what’s best for the organization to make the organization successful and secure and to reduce risk, and how we do that is we work with our peers and others within the organization, and both the CIO and CISO should certainly be working as the more strongest team together.
Bradd Busick: I think that’s spot on, and I have seen really, really awesome CIOs who went on to become CISOs. I even saw really awesome CISOs that moved into the CIO role in a different organization, and I think what it highlighted for me is that fluency where everybody understands what risk management is, and it’s no longer just a CISO’s job, or it’s no longer a CIO’s job. It’s a shared responsibility. I think we’re starting to see those ties change. At least that’s my hope.
Mark Dunkerley: Yeah, agreed, agreed. Absolutely.
Bradd Busick: Let’s shift gears here. Part of the issue with risk management is obviously that long- rich planning is really, really hard. And some would argue it’s just not even possible anymore, the old days of 10 years ago when a CEO would say, ” Mark, what’s your three- year plan?” I think the 18- month plan is also dead. How are you maintaining any semblance of financial discipline in this wildly hyper- agile environment that you and I find ourselves in today?
Mark Dunkerley: It’s not easy because even today, I mean when we work with our respective boards and our leadership, we have to have our metrics and our goals in place. So those three- year roadmaps, one- year roadmaps are things we continue to have to work towards. So we can throw some darts to the dartboard and we know where we’re going to be, but I even go back to just technology in my experience, even over the last 20 years is before technology, it was easy to do an annual budget and finance plan. Simple, we know what we wanted to do, what our goals were for as we go into next year. You introduce technology and it’s changing so fast that you cannot predict out right now with AI three to six months and what’s going to change.
Bradd Busick: That’s exactly right.
Mark Dunkerley: So asking me what I need to budget for next year, I think first and foremost, we have to be transparent about that and let others know, or when we’re requested to provide these that yes we can, but the transparency is, and making other leaders knowing those non- technical leaders is that technology’s grown so fast. You’re going to come to me next year because all of a sudden you need something, or somebody’s selling you something and you think this is going to help provide this ROI, which is great, but we didn’t budget for it. We need to now sit down and think and talk about that, and it happens all the time. So from a budget perspective, I know we do best as we go into the year ahead. We certainly have roadmaps, and those roadmaps work well as you’ve got traditional technology debt and things that you’ve got to go through in life cycle.
But as technology evolves as right now, let’s talk about current state AI and being able to use AI capabilities. It’s how do you best plan and have those conversations? Myself and the team always look to make sure we have some budget available project budgets that come up. And again, you got to be careful how much you ask for. You got to find this balance between where we need something just to be safe. But ultimately, it just comes back to, I think, the fact that as technology evolves and it becomes more the business, it’s creating those relationships to make sure that we can work together to figure out how we can work through a new project that maybe came out of nowhere because we’re not able to budget for it in advance enough.
Bradd Busick: In the absence of relationship, which you just highlighted, you cannot be a successful CIO. You can’t be a successful CISO. Relational capital is just as important as your cloud consumption. And I think the CIOs and the CISOs and the IT leaders that are listening to this, if you don’t have a relationship with the business, you’re in the wrong job. And so I love that you called that out, I think that’s brilliant. I also think this highlights the agility that we’re starting to see from the business, which is going to require IT to be just as agile.
So for example, if one of your customers came to you and said, ” Hey, there’s this new SaaS platform or this new AI overlay that tracks quality on the assembly line,” you’ve got to be ready to do that diligence, to react, to find budget for something that’s either been repurposed or partner with them to go make that joint ask because the board is now going to say, ” Okay, business owner, this is going to increase our quality of consumption or reduce our scrap by 10%. Mark, is it secure?” And if you have that relational capital, suddenly those things come together and it’s a beautiful thing when it happens. Unfortunately, it doesn’t happen all the time, so I love to hear that you’re prepping for that.
So a big theme that we’re already seeing come up across a ton of conversations this season on The Savvy CIO podcast is that there’s so much organizational and industry pressure to show up to the table with an actionable AI strategy. And more often than not, the very first question that gets asked right after, is it secure? What’s the ROI? So I’d love to get your take, the hot take. Do you think that there’s an ROI for the projects that we’re all working on around AI? What are you seeing and how are you measuring it?
Mark Dunkerley: I think there’s been use cases that have shown ROI, but I think they’re very limited versus all of a sudden there’s a lot of vendors, we’ve got these great opportunities and the business has been sold. What could potentially be this great ROI? We’re going to solve all these problems. And I think everybody’s went out and started to try and do this, throw a lot of money at it. And the reality is from a business perspective, it’s a lot harder than I think what we’ve been sold.
I think it boils down to a couple of things. Number one is we still have a lot of bad data out there, and AI is not going to fix bad data. Second one is most organizations are still running off processes from years. And if processes haven’t been optimized or reviewed to meet the current state of today and where technology is, again, AI’s not going to fix that. So when we look at the business side, I think we’ve still got a long way to go when we’re trying to use AI to better the business and their services. There is opportunity. I know as we look at AI agents and the agentic component comes along, but there’s still some foundational fundamental things that need to be resolved before I think we can truly be successful with AI in the business side.
Now, on the productivity side, this is evolving fast. I mean, we talk about ChatGPT, Copilot, and all those tools, this is where organizations should be focusing right now on how they work with their users to get the productivity out of these tools because it’s shown. The productivity’s there, the capability’s there, and we all have so much going on. We have so much repetitive work, and these tools are allowing us to really, I think, get out of some of that tedious day- to- day work and focus on the strategic things that we need to be for the business because it’s the same story, we’ve got to do more with less.
Bradd Busick: That’s right.
Mark Dunkerley: Now the challenge is everything we’ve done in technology over the last 20, 30 years is the technology now is there. Well, guess what? It’s the human factor now that we need to work through. It’s the change, it’s the adoption, and that’s where we got to focus on and really look towards as we look at the productivity side. How do we build our programs to build that adoption to show the value, how it supplements what we do, and how it’s going to continue to make our jobs more efficient as we move forward? I think that’s where the focus needs to be right now is we try and figure out what the business side looks like as we look at our data, our processes, and how we can bring in AI to be more efficient. The ROI on that side, I think we’re still struggling to find personally.
Bradd Busick: Yeah, I think that’s well said. Someone said to me on the productivity side of the house, ” The way that we’re going to be able to measure the impact of productivity tools is that we’re going to see a decrease in divorce rates because now people aren’t going to work 80 hours a week, they’re going to work 60 and be able to focus that 60 on the strategic to your point.”
Mark Dunkerley: I love that.
Bradd Busick: I thought that was an interesting metric.
Coca- Cola Bottlings’ Sales & Services is huge. I mean, you guys have a ton of moving parts across an enormously varied array of services and environments, and yet you guys actually move as one pot. I mean, you guys move and act cohesively. You and your role get to have a cool viewpoint across 50 plus bottlers to see what works and what doesn’t work at scale every day. What do you think is the most consistent mistake that you’re seeing IT leaders make when it comes to managing spend and maybe some of those hidden costs?
Mark Dunkerley: I think as we just look over the years, and I think it’s pretty consistent across the board. I don’t think it’s really unique. But I think as we look at the life cycle, I mean, I can go back 20 years, and the hidden costs, the hidden spend was around just traditional, ” Hey, I need an application.”
” Well, how are you going to host that?”
” Oh, I need a server. I need storage.” And that’s the old school way. And then all of a sudden the last five, 10 years, everybody’s transitioned into the cloud.
Bradd Busick: Yeah.
Mark Dunkerley: And then it’s like, ” Oh great, let’s just spin up the cloud.” And if larger organizations, you start having to deal with shadow IT and these consumption costs. And even if you have a good, governed cloud infrastructure team, you still are challenged with the cloud itself and consumption costs is very challenging, and it takes a lot to have to manage those costs. So I do see a lot of those in this still organizations that are traditional on- prem moving to the cloud and trying to manage subscription costs, trying to understand what those are.
Now today, obviously AI is the biggest one. Now we’re starting to see our AI vendors. We’ve started with some sort of licensing, but the cost for them is starting to change to more this token- based, and I don’t think anybody knows how to calculate AI costs when we’re looking there from token- based costs and also things we’re trying to figure it out. That one, everybody’s asking the question. I think one of the other bigger ones as well that everybody’s still dealing with, I don’t think anybody’s got beyond this, but it’s like technical legacy debt. We still have legacy servers out there, end of life servers, trying to get away from those, trying to move on from those.
Old applications that haven’t been modernized using old type of authentication, how do you secure those and isolate those? I mean, as you go through the technology debt and the legacy side, I mean, I think that’s something consistently that everybody continues to be challenged with. And especially as we have more and more risk as it relates to cybersecurity, it’s becoming more and more challenging and we need to move faster and faster, and we need to modernize quicker and quicker, and we need to be able to be as current as possible. And that seems to be very consistent across the board in every organization right now.
Bradd Busick: It does, and this is, I think, the beautiful tension, which is CEOs, CFOs, boards are like, ” Hey, we need to have AI,” except they haven’t invested enough to even get you to the point where you can say yes to AI. It’s like putting really crappy gas in a Ferrari. It just doesn’t make any sense. And so to your point, and I think for our listeners, being thoughtful about remediating some of that technical debt, not saying yes to AI until you have the right strategy around identity, until you have the right strategy around authentication, and just some of the basics that most shops haven’t even had a chance to get to because they’ve been focused on keeping the lights on. And so it’s asking someone to hyper jump into strategy when you haven’t spent the time just to get the basics down.
Mark Dunkerley: Agreed. I think that’s where the security side really helps me a lot because the security and risk side, I think, is really leaning more on to those foundational components that we need to be focused on. Identity best practices, and how should we be authenticating with multifactor patching. Traditionally, you’re looking at a 30- plus- day patching cycle. Well, guess what? If there’s a patch release, I need it installed now. That’s the mentality you need to think about. Getting current modernization, all those things lean really from the cybersecurity side and following those frameworks to help lean back into what needs to help support. Becoming more modern to help support, to your point, these newer initiatives that the boards, and executive leaders are saying, ” Hey, we need to do this now while we still have some foundational things.”
And I think it goes back to as leaders is how do you make sure and put yourself in a position as a CIO and CISO to be able to go back and say, ” Well, we still have some things to do.” And I use this on the security side with my CISO hat, is bringing the data and the facts to the table, and that tends to go a long way. It’s not about conversation, it’s how do I actually articulate it in a way that can go to the business level? And for me, it’s statistics, it’s data, what I can bring in front of them to show where we are and why we need to do this to help build that story.
Bradd Busick: So for that CIO right now that’s listening to this conversation and they’re getting crushed with budget pressure or they’re below 3% of net revenue, which means bare basics, on their back foot and trying to react instead of mitigating, what’s that one piece of advice that they need to start doing or stop doing to shift that momentum and get in front of the issue rather than chase it?
Mark Dunkerley: You mentioned this earlier on, but shifting our programs and mindset to be more proactive. If you look at IT over the years, we’ve continued to be in this reactive state, and that goes back to those hidden costs. I mean, trying to articulate that all of a sudden we need to do something now, but I don’t have resources and how I work around that. And again, it’s not easy to get from that, but from the security side, I put a big emphasis on proactive versus reactive and how do we position ourselves up for success long- term? And it’s also shifting that mindset that it’s not just the CIO responsibility or CISO responsibility. We’ve had the issue out there over the last few years when it’s a security incident, CISO’s going to lose his job.
Bradd Busick: Right.
Mark Dunkerley: Well, that needs to change and that’s part of the mindset. And how do we shift this responsibility and accountability away from one person, from the CIO and the CISO to the executive leadership and the board? And it’s how you bring that visibility. The way I do it, and we do it in the cybersecurity program, and it should be across the board, is how do you best govern your programs? Governance, risk, and compliance is one of the most important programs.
And that can apply across beyond cybersecurity, same as the CIO from a technology. How do you present and govern the program that shifts that responsibility from one person to more broadly the entire business? And that’s where it should sit ultimately. So yeah, that’s sort of my thought. There’s data out there. I think we have enough in the community. We’ve been doing this a long time now that I think we know how we can help best position ourselves for more success than what we have in the past.
Bradd Busick: I love that. Yeah, I actually feel like the future’s really bright, and I love the word that you hit on, which is community. I have a WhatsApp string of 87 CIOs that I’ve worked with for some of the biggest systems in the country, and this is how decisions get made. They would simply say, ” Hey, are you using Product X? And if it’s good enough for Coca- Cola, it’s going to be good enough for us.” And so that’s sometimes how the dialogue goes.
And obviously, when CrowdStrike happened, and when the latest zero- day is there, it’s fun to see the community come together. And I actually, that gives me a lot of hope for the future. So Mark, it’s been a pleasure chatting with you today. Thank you so much for joining us on The Savvy CIO.
Mark Dunkerley: Yeah, I’ve thoroughly enjoyed this, Bradd. I appreciate the time and opportunity, and thank you all out there.
Bradd Busick: I load my time with Mark today. Here’s what I heard that I think is really worth taking note of. The old swim lanes and silos are gone, I think merging those into a single lane of optimization is wildly important. Mark highlighted the importance of business relationships. You can tell by Mark’s demeanor that he understands the business. He understands the relationships, and he would never send a business partner to the board by himself. He would go in tandem, and that only happens through shared experience, planning, and partnership. Mark is able to turn on a dime because he doesn’t have an 18- month roadmap. At best, he probably has a six- month roadmap of capabilities that he thinks would support the business, not because he made them up, but because of his partnership with the business. And they’re the ones that told him, ” Hey, these are the things that we might want to be able to do.” So I loved Mark’s take on this and to get some time with him to talk about how Coca- Cola does it.
That’s all for today. Thanks so much for listening. Please follow us so you don’t miss an episode. This has been The Savvy CIO, brought to you by Park Place Technologies. If you want to learn more about Park Place, go to www. parkplacetechnologies. com.
And now, one last word from our guest. So Mark, as you know, the show is called The Savvy CIO. One simple question, what’s the savviest choice you’ve made in your career to date?
Mark Dunkerley: That’s a good question to put me on the spot. The savviest choice I’ve made to date, I think, was to lean into that cybersecurity role. It’s really helped me grow, evolve, and I think it’s going to help me be a better leader across the technology function as I move forward.
Bradd Busick: 100% bilingual. Business and security, it’s a winning combo.
I’m your host, Bradd Busick, and as always, IT shouldn’t just be at the table, IT is the table.
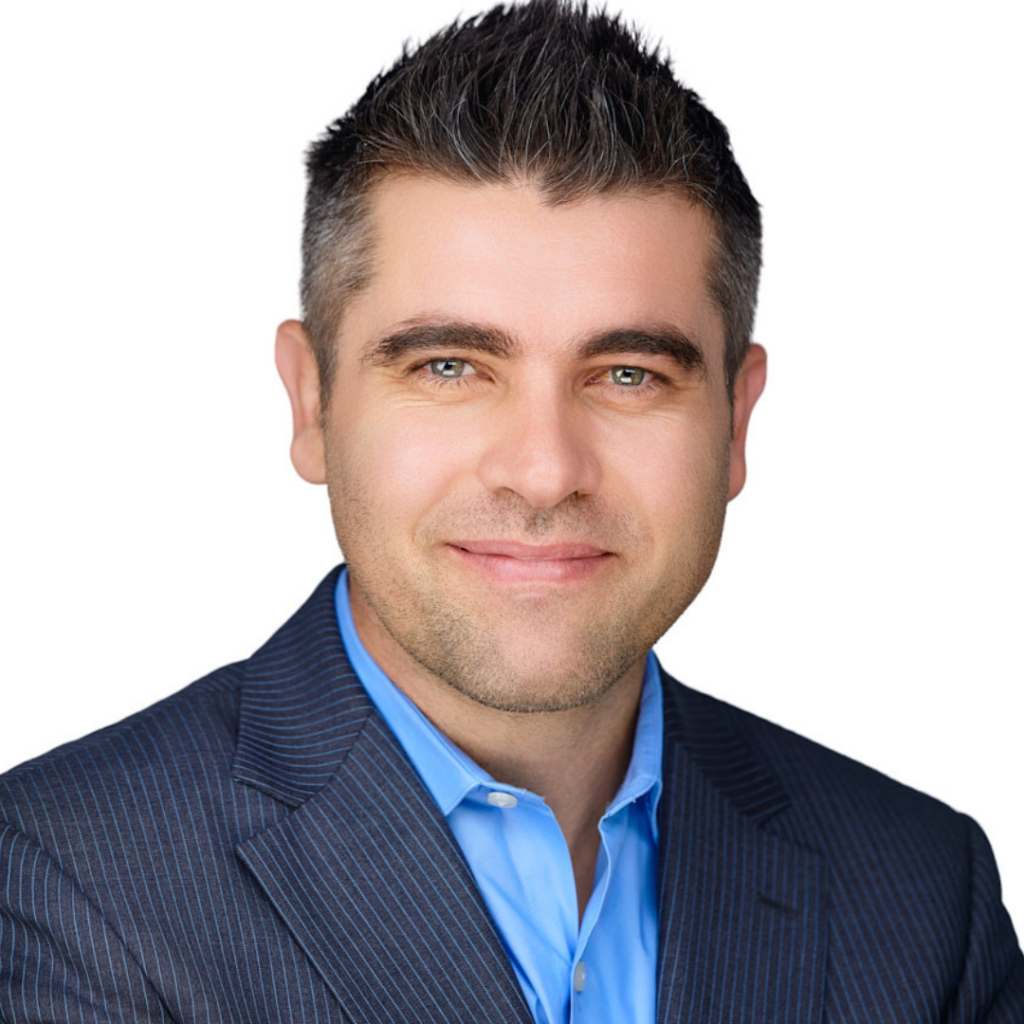
Mark Dunkerley
Guest Biography
Mark Dunkerley is a seasoned cybersecurity and technology executive with 20+ years of experience across higher education, healthcare, and Fortune 100 organizations. He specializes in enterprise architecture, IT operations leadership, and delivering resilient, scalable cybersecurity programs. Mark has led enterprise technology functions spanning infrastructure, platforms, and service delivery, aligning IT strategy with business outcomes. He holds an MBA and multiple industry certifications and is an active thought leader, keynote speaker, advisory board member, and published author. Recognized globally, he was named a Top Cybersecurity Leader (2022), Top Global CISO (2024, 2025), and a 2026 OnCon Icon Award winner for Information Security.